OpenAI continues to strengthen corporate clients' trust in its solutions: developers can now switch model operations to a special mode in which user data is not stored permanently, and the processing itself undergoes an additional security review.
What is zero data retention mode
Zero data retention mode is an option that guarantees that requests and responses are not saved on the provider's servers after processing is complete. Unlike standard usage, where data may be used to improve the service for a limited period, here the information is deleted immediately or never written to disk at all.
For businesses, this means lower risks of confidential data leaks, easier compliance with strict regulatory requirements, and the ability to work with sensitive information—from medical records to financial reports. In essence, the client gets the same model capabilities, but with behavior closer to local computing.
How it works
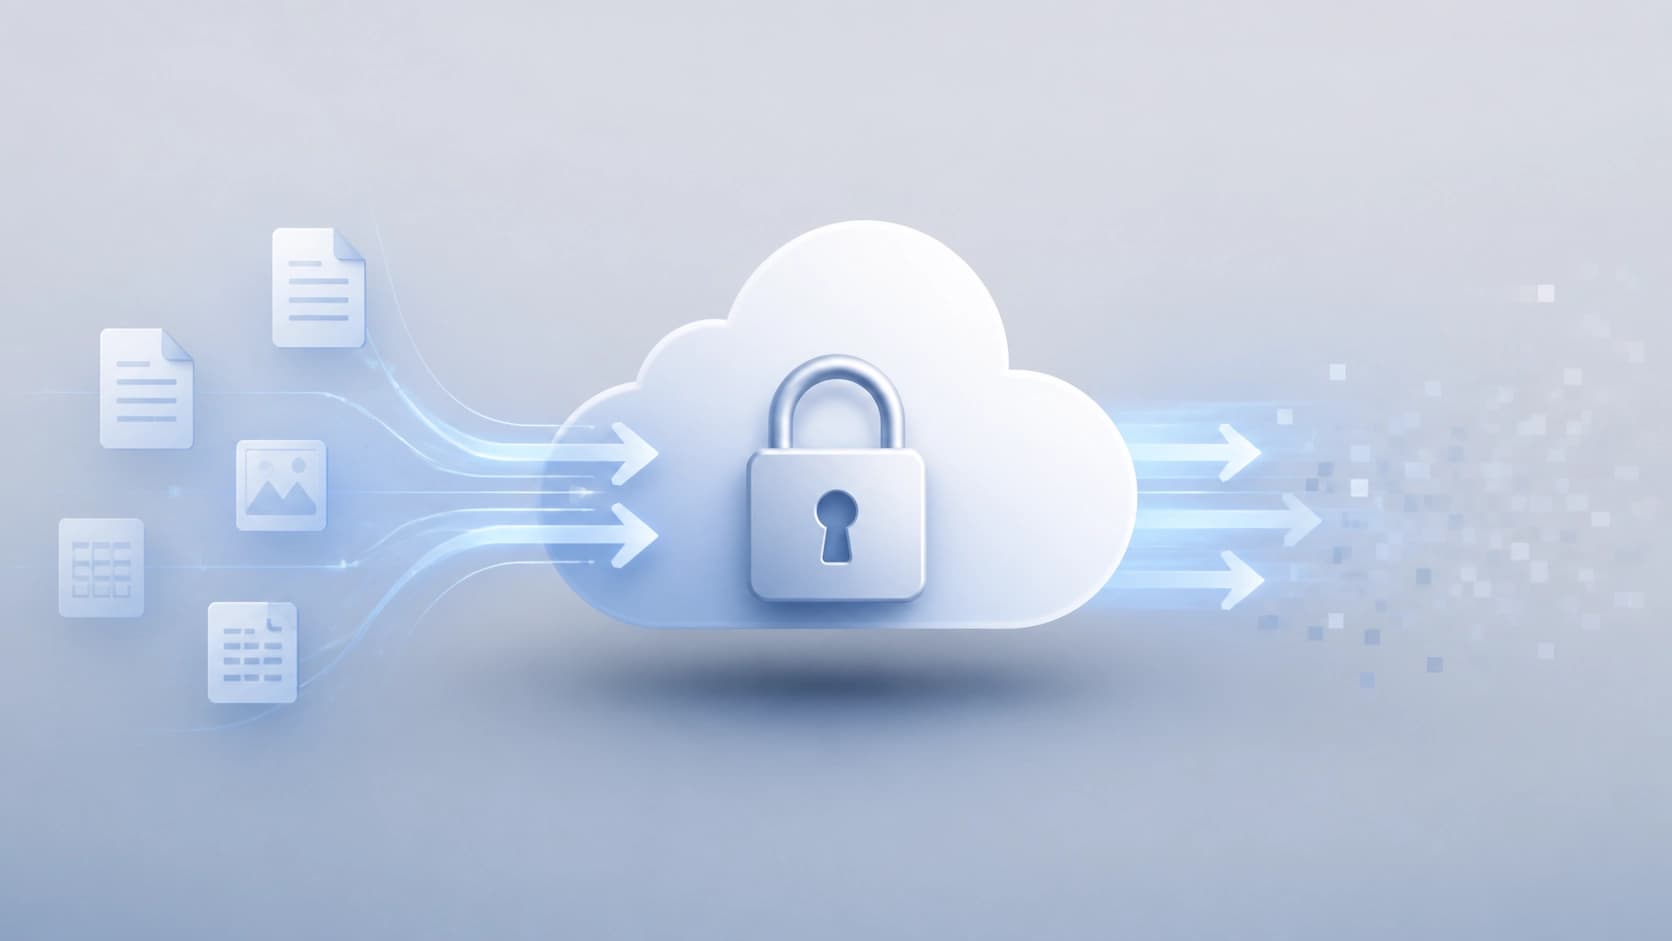
Technically, the mode is built on isolating the compute process and prohibiting any write operations except those necessary to fulfill the request. After the response is sent to the user, all temporary buffers are cleared, and when logging is enabled, no logs are created. This is not just encryption—it is a complete rejection of persistent storage, including backups.
It is important to understand the difference between confidentiality and privacy: encryption protects data from interception during transmission, but does not prevent the provider from reading it on their side. Zero data retention mode closes this gap as well, removing the question of who can access the processed information and when.
Security review for enterprise clients
As a separate step, OpenAI introduced a private security review process. This is not a one-time certification, but an ongoing audit cycle that takes place before large customers are onboarded and is repeated when the configuration changes. The review includes architecture analysis, penetration testing, and an assessment of compliance with industry requirements.
This approach allows companies in regulated industries—banks, insurance organizations, government agencies—to engage external auditors and build their own compliance on the basis of official review results. From the client's perspective, this removes the need to independently investigate every technical aspect of the API's operation.
What the review includes
- Verification of data access policies and employee roles.
- Checking the correctness of zero-retention implementation at the code level.
- Monitoring security logs without storing request contents.
- Documenting incident response procedures.
Who benefits from this
First of all, zero data retention mode is designed for organizations that process personal data of EU citizens or patients in the US, where strict privacy laws apply. But small startups can also benefit: using this mode shows clients that the product takes privacy seriously and helps win tenders.
At the same time, limitations should be considered. Zero retention may exclude some fine-tuning capabilities on historical data and also complicates error analysis after an incident. Therefore, before choosing a mode, it is worth clearly defining what types of data are processed and whether their further use is required.
Conclusion
The launch of zero data retention mode and private security review makes working with cloud AI services more predictable and transparent for large businesses. OpenAI is clearly signaling to the market that it is ready to adapt its products not only to technical requirements, but also to the legal norms of different countries. It remains to be seen how quickly other cloud model providers will adopt this practice, and it will become obvious that privacy is becoming the new standard in the artificial intelligence industry.